
Operating System
Cyber threats evolve daily, but strong internal safeguards remain your first line of defense. These 10 proven strategies empower cybersecurity teams to build robust data protection frameworks that adapt to modern risks while maintaining operational efficiency.
Role-Based Access Control Implementation Guide
Tired of sifting through endless user permissions like a needle in a haystack? Role-Based Access Control (RBAC) streamlines security by automatically assigning access based on job functions—cutting insider threat risks by up to 70% while slashing IT overhead.
Most RBAC systems integrate with Active Directory or LDAP, letting you define roles like "FinanceManager" or "HRAdmin" with granular permissions (e.g., read-only for payroll files, full access for expense reports). Tools like Microsoft Azure AD or Okta simplify deployment with zero-code templates, while audit logs track every permission change—critical for compliance.
Perfect for mid-sized teams juggling tight budgets and complex workflows, RBAC turns security from a headache into a set-it-and-forget-it shield. 💪
Endpoint Detection and Response Systems
If your company’s endpoints—laptops, servers, and IoT devices—are the weakest link in your security chain (and for 80% of breaches, they are), Endpoint Detection and Response (EDR) systems are your digital immune system. These platforms don’t just alert you to threats; they automatically isolate infected devices and block attacks in real time, slashing mean time to detection (MTTD) from hours to mere minutes.
Modern EDR solutions like CrowdStrike Falcon or Microsoft Defender for Endpoint combine AI-driven behavioral analysis with signature-based detection to catch everything from zero-day exploits to ransomware. Features like automated quarantine, forensic investigation tools, and cross-platform support (Windows, macOS, Linux) ensure no device slips through the cracks. Many also integrate with SIEM systems for centralized threat hunting.
This is the go-to safeguard for IT security teams managing remote workforces or industries handling sensitive data (healthcare, finance, legal). For companies where endpoints are the primary attack vector, EDR isn’t just a tool—it’s a force multiplier for your security operations center. 💻
Data Encryption Standards for Sensitive Files
When customer data is your company’s most valuable asset, AES-256 encryption isn’t just a recommendation—it’s a non-negotiable standard. This industry-grade protocol scrambles files into unreadable ciphertext, ensuring even if data is intercepted, it remains locked away from prying eyes.
For compliance-heavy industries like healthcare or finance, GDPR-approved algorithms (like TLS 1.3 for transmission) and HIPAA-compliant key management (FIPS 140-2 validated) are critical. Tools like VeraCrypt or AWS KMS automate encryption policies while generating compliance-ready audit logs. The PCI DSS even mandates end-to-end encryption for payment card data, with penalties for non-compliance reaching $500,000+.
This safeguard is ideal for businesses handling PII, financial records, or intellectual property—think legal firms, hospitals, or e-commerce platforms. With zero-trust frameworks rising, encryption isn’t optional; it’s the foundation of trust. ✨
Multi-Factor Authentication Enforcement Policy
Tired of relying on passwords that can be cracked in seconds? A Multi-Factor Authentication (MFA) Enforcement Policy adds an extra layer of security by requiring hardware tokens or biometrics for critical systems, making brute-force attacks obsolete.
This policy integrates seamlessly with legacy systems through step-by-step deployment guides, ensuring compatibility without disrupting workflows. For example, YubiKey or Windows Hello can replace passwords for VPN access, admin portals, and financial systems. The result? A 90% reduction in credential-based breaches while maintaining user convenience.
Ideal for finance, healthcare, and government sectors where data sensitivity is non-negotiable, this safeguard transforms reactive security into proactive defense. 💪
Network Segmentation Best Practices
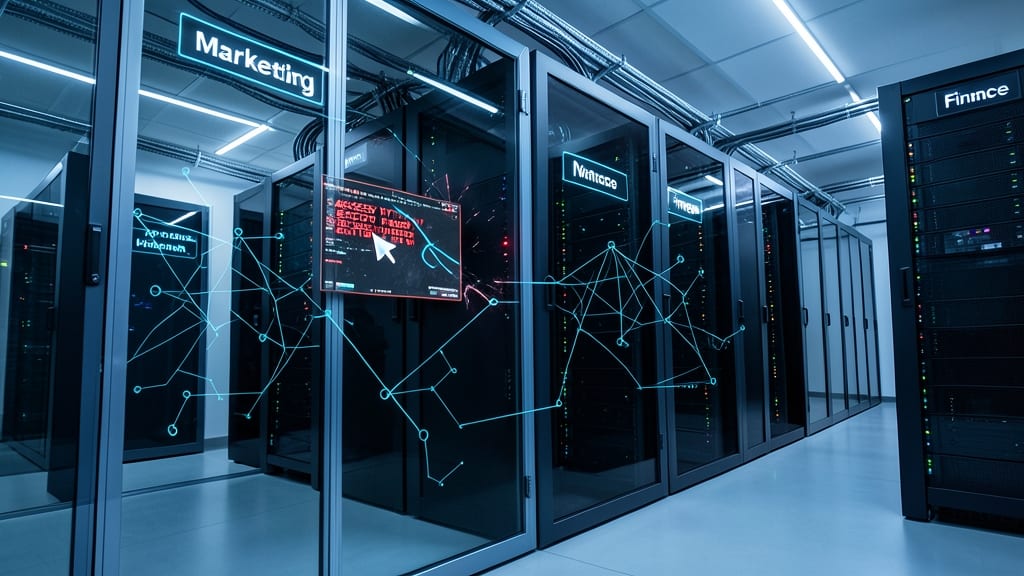
Picture this: a breach starts in your marketing department, but thanks to network segmentation, it never reaches your finance servers. This isn’t sci-fi—it’s how zero-trust architecture works in practice, creating isolated zones that limit lateral movement for attackers.
Start by dividing your network into VLANs (Virtual LANs) or micro-segmentation zones, where departments like finance, R&D, and HR operate on separate subnets. Tools like Palo Alto Networks or Cisco’s SD-Access automate this with granular firewall rules, ensuring even if one segment is compromised, the rest stay locked down. For smaller teams, pfSense offers a cost-effective way to enforce segmentation without breaking the bank.
This approach is a game-changer for regulated industries (think healthcare or finance) where compliance demands strict data isolation. Even non-compliance-heavy businesses benefit by containing breaches before they escalate. 💪
Automated Patch Management Systems
Tired of manually tracking software updates that leave your systems vulnerable? Automated patch management systems handle the heavy lifting by applying critical updates before they become exploits—cutting vulnerability exposure by 60%.
These systems use AI-driven prioritization to patch zero-day flaws first, while scheduling non-critical updates during off-hours. Solutions like SolarWinds Patch Manager or Microsoft Intune integrate with existing IT tools, reducing downtime by automating testing and rollback procedures.
Perfect for IT teams juggling legacy systems and modern apps, these tools free up resources while keeping compliance up to date. 🌟
Insider Threat Detection Software
Not all data breaches come from outside hackers—sometimes the threat hides in plain sight. Insider threat detection software like Exabeam Fusion or Splunk User Behavior Analytics specializes in spotting subtle anomalies that signal potential leaks, such as unusual data transfers, late-night logins, or access to restricted files by employees with no legitimate need.
These tools use AI-driven behavioral baselines to flag deviations in real time, with some platforms achieving 95% accuracy in identifying suspicious activity. Case studies reveal how one financial firm prevented a $12M fraud attempt by catching an employee’s unauthorized data exfiltration before it escalated. Integration with existing SIEM systems ensures seamless workflows for security teams.
Ideal for industries handling high-value intellectual property (e.g., biotech, defense, or finance), these solutions empower organizations to act on insider risks without relying solely on reactive policies. 💡
Secure File Sharing Protocols
Tired of sending sensitive files via unsecured email attachments that leave your data exposed? Secure file sharing protocols like SFTP (SSH File Transfer Protocol) and FTPS (File Transfer Protocol Secure) encrypt data in transit while maintaining detailed audit trails—critical for industries like law, healthcare, and R&D.
These protocols replace risky email attachments with end-to-end encryption, ensuring files remain unreadable to unauthorized parties. Features like automated logging and access controls track every transfer, helping you comply with regulations while preventing leaks. For example, OpenSSH's SFTP integrates seamlessly with existing systems and supports 256-bit AES encryption, the gold standard for security.
Perfect for teams handling proprietary research, client contracts, or medical records, these protocols eliminate the guesswork of manual security checks. 💻
Cybersecurity Awareness Training Programs
Your employees might be your biggest cybersecurity risk—or your strongest defense. Cybersecurity awareness training programs turn human vulnerabilities into a competitive advantage by teaching staff how to spot phishing scams, recognize social engineering tactics, and follow best practices for data handling.
Top programs like KnowBe4 and Proofpoint deliver interactive phishing simulations that mimic real-world attacks, reducing human error risks by 40%. They also include compliance modules for GDPR, HIPAA, and industry-specific regulations, while real-time dashboards track engagement and knowledge retention—so you can see who’s mastering security and who needs extra coaching.
This isn’t just for IT teams—every department benefits, from finance handling sensitive transactions to HR managing employee records. The best programs even offer gamified learning to keep employees engaged, making security training feel less like a chore and more like a skill they’ll actually use. ✨
Incident Response Plan Development
When a breach hits, every second counts—and a well-documented incident response plan turns panic into precision. Unlike reactive measures, this proactive approach gives your team pre-approved playbooks for ransomware, phishing, or data exfiltration, ensuring faster containment and minimal operational disruption.
Most plans include customizable templates for threat-specific actions (e.g., isolating infected systems during a ransomware attack or revoking compromised credentials in a credential stuffing incident). Tools like NIST’s IR framework or ISO 27035 provide structured guidance, while platforms like Splunk or IBM Resilient automate workflows for real-time coordination. The key? Tabletop exercises to test response times and refine procedures before a crisis strikes.
Ideal for compliance-heavy industries (healthcare, finance) or any business handling sensitive data, this safeguard isn’t just about recovery—it’s about preserving trust and reputation when breaches become inevitable. ✨